
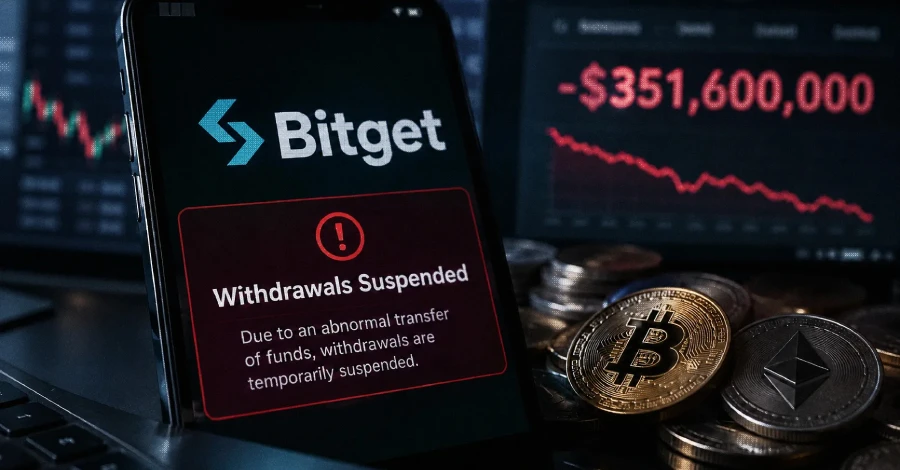
Cryptocurrency exchange Bitget has revealed that cyber operators suspected of ties to North Korea executed a major breach against its infrastructure, siphoning approximately $351.6 million from hot and warm wallets.
Unauthorized Wallet Activity Detected
According to an official disclosure issued on social media platform X, Bitget’s automated defense protocols flagged abnormal network activity on September 24, 2026, at 18:31 UTC. The detection identified unauthorized outflows directly impacting a limited segment of the platform’s hot wallet infrastructure.
Cold Wallets and User Reserves Remain Protected
Bitget clarified that while the incident led to substantial losses across warm and hot storage, its offline cold storage facilities remained completely safe. The exchange emphasized that the overwhelming majority of assets hosted on the platform were insulated from the backend compromise.
About The Author